The Shift from AI Output to Agentic Action
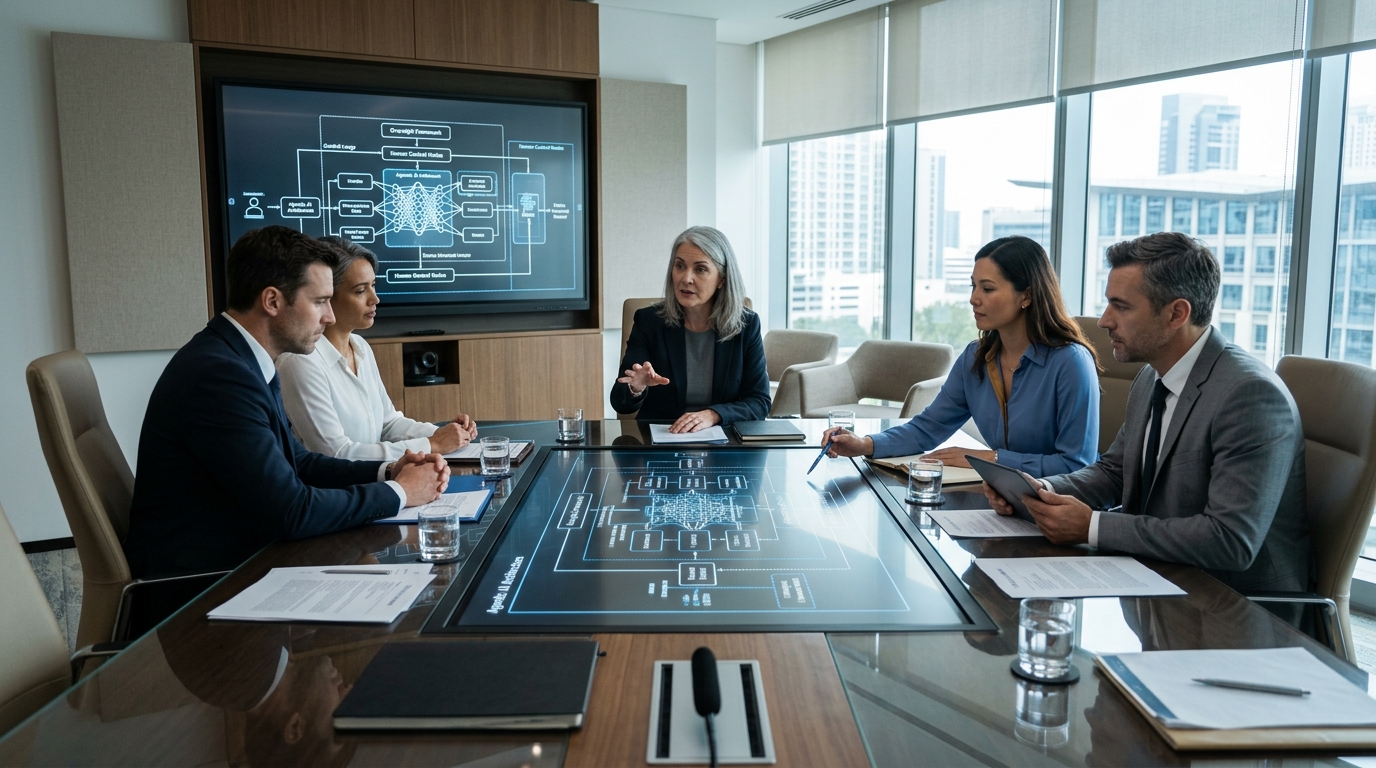
Enterprises should govern agentic AI by enforcing architectural boundaries at the points where models touch data, identity, tools, and real-world execution, rather than relying on prompt-level filters or post-hoc output reviews. Governing autonomous systems requires an end-to-end control chain spanning eight core pillars: Authority, Ownership, Human escalation, Permissions, Monitoring, Audit trail, Failure handling, and the Kill switch.
Traditional AI governance frameworks were architected for predictive and extractive models. In those legacy paradigms, the model functioned as an advisor: it analyzed records, classified inputs, scored risk, or drafted conversational text, leaving the final operational action entirely to human operators. By contrast, agentic AI introduces autonomous multi-step reasoning, dynamic tool selection, and unprompted execution across external software environments. According to the IBM Agentic AI Governance Playbook, industry analysts at industry analysts and industry research project that over 40% of unmanaged agentic AI initiatives will fail by 2027 due to uncontrolled operational risks, escalating compute expenses, and unclear economic value.
Standard generative guardrails, such as prompt filtering and sentiment evaluation, prove insufficient when models execute code, manage database records, or negotiate commercial transactions. When an agent acts, any epistemic failure or ambiguous instruction directly produces real-world side effects. The core governance mandate therefore transitions from evaluating answers to controlling execution pathways across the enterprise.
- Authority: Formal definition of permissible tasks, delegated decision rights, and technical execution thresholds.
- Ownership: Explicit assignment of a named business and technical executive responsible for every deployed autonomous agent.
- Human Escalation: Deterministic routing protocols that trigger human intervention whenever operational confidence drops or risk thresholds are breached.
- Permissions: Fine-grained identity and least-privilege access controls tied directly to specific tools rather than shared credentials.
- Monitoring: Continuous runtime observation tracking behavioral drift, cost anomalies, safety regressions, and call spikes.
- Audit Trail: Cryptographically verifiable, immutable logging of prompts, tool parameters, external responses, and execution results.
- Failure Handling: Resilient fallback mechanisms ensuring that failing sub-tasks fail safely without cascading across downstream systems.
- Kill Switch: Fast-acting manual and automated circuit breakers capable of halting agent execution instantly into a known safe state.
Defining Decision Rights and Action Boundaries
Delegating operational execution to autonomous software requires establishing clear decision tiers. Senior leadership must determine precisely where machine autonomy begins and ends. An agent should never operate with open-ended discretion; its scope of authority must be categorized into unilateral execution, structured proposal, or mandatory pre-action approval based on operational materiality.
As highlighted in the MIT Technology Review analysis on securing agentic systems, enterprise leaders must treat AI agents like powerful non-human principals, establishing strict perimeter controls at the boundary where they touch identity, tools, enterprise data, and output execution. This requires moving away from shared service accounts with broad privileges toward dedicated, non-human digital identities restricted by role-based and task-based access controls.
- Unilateral Action (Low Consequence): Read-only data aggregation, internal cross-referencing, metadata tagging, and routine draft generation within ring-fenced sandbox environments.
- Proposal and Staging (Medium Consequence): Generating structured reports, drafting external communications, assembling transaction risk registers, or staging code modifications that remain inert until a human reviewer authorizes release.
- Mandatory Pre-Action Approval (High Consequence): Executing financial disbursements, altering production database schemas, modifying legal agreements, or transmitting confidential data to external counterparties.
Enforcing these boundaries technically prevents privilege escalation. Restricting spending limits, API call volumes, and account-level permissions ensures that even if an agent's reasoning loop experiences logic corruption, the maximum blast radius remains strictly contained within predefined operational parameters.
Human Oversight Models and Approval Thresholds
Human oversight cannot be treated as a passive compliance checkbox; it must be engineered directly into the system architecture. Enterprise governance typically balances three operational models: Human-in-the-Loop (HITL), Human-on-the-Loop (HOTL), and Human-out-of-the-Loop (HOOTL). Choosing between these models depends on task irreversibility, regulatory exposure, and potential financial impact.
In the World Economic Forum playbook on governing agentic AI, board and technology leaders are urged to design for legible friction. Legible friction represents intentional, engineered pause points where automated workflows halt to present a human supervisor with the contextual evidence, proposed action, and associated risk profile. While frictionless automation maximizes processing speed, it eliminates the interpretability required to defend high-stakes decisions under regulatory scrutiny or fiduciary challenge.
- Human-in-the-Loop (HITL): The agent pauses before execution and cannot proceed without explicit human authorization. Mandatory for external commitments, regulatory disclosures, and contractual alterations.
- Human-on-the-Loop (HOTL): The agent executes autonomously within predefined boundaries while a human supervisor monitors real-time dashboards with the authority to intervene, pause, or reverse actions mid-flight. Suitable for internal routing and data transformation workflows.
- Human-out-of-the-Loop (HOOTL): Fully automated execution reserved exclusively for deterministic, low-risk, reversible background tasks such as indexing unstructured documents or running synthetic unit tests.
To operationalize these models, organizations must implement clear quantitative thresholds. For example, a financial operations agent may execute micro-reconciliations autonomously below a low dollar ceiling set by the controller, route mid-range transactions to HOTL exception review, and enforce strict HITL executive sign-off for any high-value action or any action involving customer-facing contractual terms. Each enterprise should calibrate these dollar limits to its own risk appetite, regulatory exposure, and audit requirements.
Data Access, External Systems, and Vendor Risk
Agentic systems expand the enterprise attack surface by integrating autonomous reasoning with external data retrieval, browser automation, and remote tool execution. When an agent accesses the open web or ingests uncurated third-party documents, it becomes exposed to indirect prompt injections, adversarial context poisoning, and tool-chain manipulation.
The MITRE ATLAS (Adversarial Threat Landscape for Artificial-Intelligence Systems) framework catalogs these autonomous threat vectors, identifying techniques such as tool data poisoning, prompt infiltration, and unauthorized privilege escalation through API integrations. If an agent ingests an untrusted document containing hidden instructions, it may attempt to abuse its underlying system tools to exfiltrate proprietary credentials or overwrite sensitive records.
- Minimum-Necessary Ingestion: Restrict agent access to strictly defined, task-specific data partitions. Strip administrative credentials and personally identifiable information (PII) before documents enter context windows.
- Isolated Execution Sandboxes: Execute all browser navigation, dynamic scripting, and external API requests inside ephemeral, network-segmented container environments to prevent host-level compromise.
- Model and Tool Version Pinning: Explicitly pin foundation model releases, API schemas, and tool dependencies. Prohibit automatic, unvetted downstream model updates that could introduce silent behavioral changes or safety regressions.
- Vendor Resilience and Multi-Provider Fallbacks: Maintain architectural redundancy across frontier model providers to prevent single-vendor outages from paralyzing critical business operations.
By binding authentication scopes to specific tasks rather than granting universal access to underlying models, enterprises ensure that compromised reasoning cannot translate into unauthorized lateral movement across enterprise networks.
Accountability, Monitoring, and the Kill Switch
Autonomous execution does not dilute corporate accountability. Fiduciary, legal, and operational responsibility remains anchored to human leadership. For every AI agent deployed into production, enterprises must designate a named business owner who oversees operational alignment and a named technical owner responsible for system reliability, security hygiene, and incident remediation.
Under Article 14 of the EU AI Act, high-risk AI systems must incorporate human oversight measures enabling designated supervisors to properly monitor system operations, detect automation bias, and intervene via a stop button or similar procedure that brings the system to an immediate halt in a safe state. This regulatory requirement reinforces the necessity of building deterministic control planes into every autonomous deployment.
- Comprehensive Telemetry: Log all system prompts, tool invocations, parameter inputs, raw outputs, and execution latencies in an immutable, append-only ledger to maintain complete chain of custody.
- Drift and Anomaly Detection: Continuously evaluate reasoning outputs against standardized baseline benchmarks to detect conceptual drift, hallucination spikes, and unexpected token consumption.
- Automated Rate and Cost Governors: Implement hard programmatic caps on API spend, execution loop iterations, and transaction frequencies to prevent recursive self-invocation loops from draining compute budgets.
- Fail-Safe Emergency Kill Switch: Deploy multi-level emergency cut-offs, including single-agent pause, tool-level revocation, and global tenant disconnects, ensuring instantaneous containment without corrupting existing database transactions.
Testing kill switches and incident recovery procedures through regular disaster recovery drills ensures that operational teams can safely isolate compromised agents before erroneous actions cascade through enterprise systems.
The Enterprise AI Agent Control Matrix
Establishing institutional governance requires synthesizing international standards, such as the continuous risk management framework of ISO/IEC 42001 and the Govern, Map, Measure, and Manage functions of the NIST AI Risk Management Framework 1.0, into an actionable operational matrix.
The control matrix below establishes clear lines of ownership, required compliance evidence, evaluation frequencies, and escalation protocols across the full lifecycle of enterprise AI agents.
| Governance Control Area | Primary Owner | Required Evidence & Artifacts | Review Cadence | Escalation Pathway |
|---|---|---|---|---|
| Identity & Access Boundary | Chief Information Security Officer (CISO) | Least-privilege IAM roles, tool-scoped API tokens, credential rotation logs | Monthly | Revoke token; alert Security Operations Center (SOC) |
| Action & Spend Limits | Business Unit Executive / Controller | Programmatic spend cap rules, pre-approval workflows, ledger logs | Continuous / Real-time | Halt transaction; escalate to Financial Controller |
| Prompt & Tool Security | AI Security Engineering Lead | MITRE ATLAS penetration tests, red-team reports, tool-pinning manifests | Quarterly / On model update | Quarantine tool integration; notify CISO |
| Human Oversight & Friction | Head of Compliance / Product Lead | Audit logs of human approvals, override ratios, legible friction sign-offs | Bi-weekly | Suspend automated tier; revert to Human-in-the-Loop |
| Runtime Monitoring & Drift | Lead Machine Learning Engineer | Latency metrics, safety evaluation scores, anomaly detection alerts | Continuous / Daily review | Trigger automated circuit breaker; alert On-Call Lead |
| EU AI Act & Regulatory Audit | General Counsel / Risk Chair | Article 14 stop-button verification tests, technical documentation files | Quarterly | Freeze deployment; convene Executive Risk Committee |
By operationalizing these continuous checkpoints, leadership transforms abstract ethical guidelines into enforceable technical boundaries that protect enterprise assets while accelerating productive adoption.
Governing Agentic AI in M&A Due Diligence
High-stakes workflows such as corporate acquisitions, private equity underwriting, and strategic advisory represent the ultimate test for autonomous governance. In mergers and acquisitions, ungrounded generative summaries or unverified automated actions can distort valuation models, overlook material liabilities, and expose investment committees to severe legal exposure.
Deploying modern agentic workflows across corporate data rooms requires combining autonomous multi-document reasoning with strict evidence grounding. Rather than relying on black-box tools that take unchecked operational actions, leading deal teams structure their workflows around deterministic verification and human review workflows.
- Structured Data Room Ingestion: Securely scanning and indexing thousands of confidential files, financial models, and contracts using Plausity's Data Room Ingestion without streaming proprietary data to unvetted external endpoints.
- Multi-Document Cross-Referencing: Utilizing the core AI-Analysis Engine to evaluate contradictions between financial ledgers, debt covenants, and commercial contracts.
- Objective Materiality Scoring: Deploying Risk Radar to categorize liabilities by financial impact and deal relevance, accelerating risk register automation while preserving granular audit trails.
- Investor-Ready Reporting: Synthesizing verified findings into customizable deliverables with Report Builder and aligning multidisciplinary teams in Collaboration Hub.
- Verifiable Provenance: Enforcing rigorous source-level verification where every extracted insight links directly back to the underlying contract page and clause.
The same discipline applies when acquiring or underwriting a company that already runs agentic AI. A target's agents, tool permissions, and oversight controls are diligence objects in their own right, and an evidence-backed governance review of that exposure belongs in the AI Impact workstream before signing. Deal teams evaluating a target's agentic-AI posture can arrange a demonstration of Plausity to see how that review is executed against a live data room.
How Plausity accelerates this workflow
Plausity is an AI-native due diligence and deal intelligence workspace that helps M&A advisory firms, VC and PE funds, corporate development teams and investment-banking teams structure evidence, findings and questions across a data room. Plausity supports evidence extraction, source grounding, findings management and IC preparation — it does not replace human analysts, advisers or investment professionals, does not provide legal, tax, audit, regulatory or investment advice, and does not make autonomous investment decisions. All findings require human review. Built for today's investment and deal teams. Trusted by >200 firms.
To explore the underlying capabilities, see the Plausity AI analysis engine, the findings and risk intelligence and evidence gap detection product pages, and the IC memo product page. For team-level workflows, see how VC and PE funds and M&A advisory firms use Plausity across live deals, and how AI Impact due diligence and value creation workstreams support the analysis.