The 2026 tech M&A landscape: conviction over volume
What should a buyer actually diligence in a technology acquisition in 2026? In short: the deal thesis first, then the target's architecture and technical debt, the boundary between AI capability it owns and capability it rents, the rights over the data and models the valuation rests on, the security posture it will inherit, the credibility of the roadmap, and the integration burden those findings create. AI, data and cyber risk have moved from specialist annexes to the core of underwriting because they now determine whether the asset being bought is defensible or merely expensive. The discipline has shifted from collecting information to demanding evidence that reprices or restructures the deal.
The market context makes this discipline non-negotiable. In Q1 2026, TMT deal count fell 15.1% quarter on quarter to 1,359 transactions, while disclosed deal value rose 88.3% year on year to USD 446.9 billion, according to KPMG. KPMG describes a K-shaped environment in which megadeals dictate outcomes, average deals under USD 25 million are vanishing, and differentiated assets command multiples two to three times higher than less-differentiated peers. Strategic buyers drove over 90% of disclosed value. Capital is concentrating; conviction, not activity, is being rewarded.
Strategic rationale for a tech acquisition
That conviction has to be underwritten against a specific thesis, because each thesis makes different demands on diligence:
- Capability acquisitions, where the asset is talent and know-how, and diligence must prove the people and IP can be retained and transferred.
- Product acquisitions, where the asset is revenue and roadmap, and diligence must prove retention quality, pricing durability and technical debt.
- Platform acquisitions, where the asset is an operating layer, and diligence must prove architecture, scalability and integration fit.
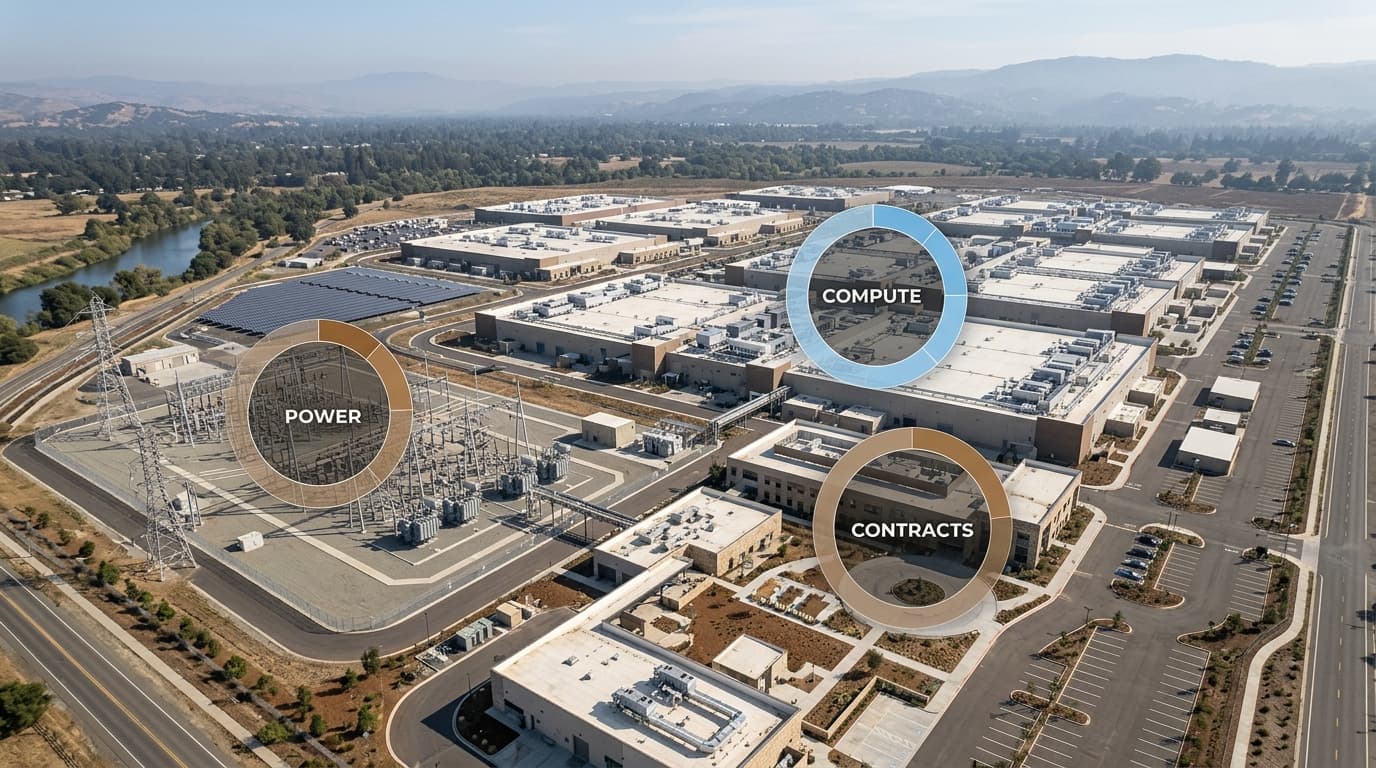
- Infrastructure acquisitions, where the asset is compute, data or network capacity, and diligence must prove cost-to-serve, supply contracts and regulatory exposure.
Buyers are no longer acquiring only products but also data, models, infrastructure and talent, assets that are difficult to validate and value during diligence. Deloitte draws the same conclusion from the AI deal wave: when the acquisition is people, code and compute contracts, the traditional clean-perimeter playbook breaks down, and hybrid structures such as acquihires, non-exclusive IP licensing and strategic partnerships now sit alongside outright acquisitions.
Technology architecture: build, runtimes, hosting and cost profile
Underwrite what the target is built on before underwriting what it will earn. That means mapping the build-versus-buy decisions behind the stack, the runtimes and frameworks in production, the hosting profile across cloud providers, and the degree of lock-in in both directions: how hard the target is to migrate, and how exposed its cost base is to a single vendor's pricing. Cloud cost-to-serve belongs in the model from day one. KPMG's Q1 2026 analysis names underestimating cloud cost-to-serve as a recurring execution risk and advises dealmakers to stress-test gross-margin durability under higher model serving and security costs before final bids.
Technical debt: the accumulated cost of shortcuts
Technical debt is the accumulated cost of shortcuts, and in a transaction it is either priced or inherited. KPMG's 2025 technology sector M&A survey of 135 deal professionals found tech debt to be a deal-shaping risk that is under-addressed in deal planning yet costly in execution. For a buyer, that gap is a margin and velocity assumption, not a footnote: it determines how much of the engineering budget the first twelve months of ownership will spend standing still. Demand the remediation backlog, the age and ownership of core components, and the last time critical systems were meaningfully refactored.
Product roadmap: credible versus speculative, gating dependencies
Judge whether the roadmap is credible and whether the team that delivers it will still be there. A credible roadmap decomposes into gating dependencies: for each milestone, what must be true technically, which engineering and data prerequisites exist today, and what must be true commercially, whether that is a reference customer, a regulatory approval or a pricing change. Speculative roadmaps state destinations without dependencies. Ask the target to walk each committed feature back to the code, data and people it requires, and treat hesitation as a signal.
- Technical gates: does the architecture, the data and the team exist to ship the milestone, or does it assume capabilities not yet built?
- Commercial gates: which customer, contract or market condition must materialise for the milestone to produce revenue?
- Sequencing gates: which milestones block each other, and what does a six-month slip do to the revenue plan?
Commercial impact: pricing durability and retention quality
Commercial impact turns the roadmap into a valuation question, and pricing-model durability is its sharpest edge. PwC's analysis of AI and software valuations notes that seat-based pricing is under structural pressure because AI agents compress the number of seats a customer needs, that net revenue retention can mask seat contraction beneath AI add-on revenue, and that gross revenue retention and cohort-level analysis are now essential diligence metrics. A revenue line that looks like expansion may be a customer paying the same for fewer humans, so cohort-level revenue analysis belongs in the diligence plan.
AI capability and disruption exposure: what the target owns, what it rents
The central AI diligence question is ownership: what does the target actually own, and what does it rent? A proprietary model trained on exclusive data, with documented evaluation and its own serving infrastructure, is a different asset from a thin wrapper orchestrating a frontier model through an API. PwC's analysis of AI and software valuations finds that defensibility now lies in domain depth, ecosystem entrenchment, proprietary context and workflow gravity rather than in the code itself, and that AI lowers barriers to entry for replaceable tools built on surface-level features. The same frontier models that power the target also arm its competitors, so disruption exposure runs in both directions.
Cybersecurity posture, active incidents and remediation
Model IP is the second test. Confirm that patents, copyrights and trade secrets in the models and training pipelines are assigned to the target, that all material contributors have executed assignments, and that no copyleft obligation forces disclosure or licensing of proprietary code or model weights. Reed Smith recommends representations that all software, models, datasets and tools comply with applicable licences, including open-source provisions, with no such copyleft exposure.
The third test is contractual protection after closing. AI-specific indemnities covering training data rights, open-source compliance and pre-close privacy violations are increasingly standard, along with longer survival periods and dedicated escrows, often 18 to 24 months, for data, IP and privacy risks. Morgan Lewis likewise documents the shift toward targeted representations, special indemnities and special escrows as transaction documents evolve to cover AI and data compliance risk. If the seller resists these mechanics, treat the resistance itself as information about the risk.
Diligence the security posture you will inherit, not the one described in the data room. The financial baseline is material: IBM's 2025 Cost of a Data Breach Report puts the global average breach cost at USD 4.44 million, with the US average at a record USD 10.22 million, and finds that breaches involving shadow AI carried an average of USD 670,000 in additional costs. For a target holding sensitive customer data, a single unremediated finding can be a seven-figure liability with regulatory tail.
Posture assessment should cover the controls that matter in a transaction: identity and access management, patching cadence, detection and response capability, and the state of any active or undisclosed incidents. Demand breach and near-miss history, penetration test results, and notification obligations already triggered with customers or regulators. A structured, nine-phase view of this workstream is set out in a modern cybersecurity due diligence framework for M&A.
The AI-specific attack surface is new and frequently ungoverned. IBM's report found that 63% of breached organisations had no AI governance policy or were still developing one, and that among those with a policy in place only 34% perform regular audits for unsanctioned AI. One in five organisations studied reported a breach involving shadow AI, uncontrolled employee use of public models. In diligence, ask which teams are using which public models, with what data, under what policy. The answer is often that nobody knows, which is itself a finding.
Finally, convert findings into deal mechanics. Every material security gap should map to one of three outcomes: a price adjustment reflecting remediation cost, a specific indemnity with a defined cap and survival period, or a closing condition requiring remediation before completion. Findings that map to none of the three have simply been transferred to the buyer at full price.
Tech-team dependency and key-person risk
Key-person risk completes the section. Deloitte is blunt on the point: talent has agency, and speed-to-retention is not a nice-to-have but existential, because deals that take months to close risk losing the very capability they were designed to secure. In acquihire-shaped deals, map the individuals whose departure would impair the asset, review their equity, notice periods and non-competes, and price the retention package into the consideration rather than discovering it in the first ninety days after closing.
Integration complexity: the pre-signing view of the integration burden
Integration is where conviction is either converted into value or written off as goodwill, and KPMG's Q1 2026 analysis warns that overpaying for theoretical AI leverage without underwriting integration friction is the fastest way to destroy value. The pre-signing view of integration should therefore be built dimension by dimension, with each diligence finding carrying an explicit integration implication rather than sitting in an appendix. The framework below is the playbook in one view:
| Dimension | What to test | Evidence to demand | Red flag | Integration implication |
|---|---|---|---|---|
| Technology architecture | Build-versus-buy, runtimes, cloud lock-in, cost-to-serve | Architecture diagrams, hosting contracts, cost per workload | Undocumented core systems, single-vendor lock-in without exit plan | Migration or renegotiation programme before synergy case holds |
| Technical debt | Share of engineering capacity consumed by remediation | Backlog, component age, refactoring history | Debt unquantified or remediation perpetually deferred | First-year roadmap slows; budget a standing remediation line |
| AI capability | Owned versus rented capability, disruption exposure | Model documentation, evaluation records, dependency map | Thin wrapper on a third-party model with no data moat | Capability can be replicated or revoked; value case resets |
| Data and IP | Rights, provenance, training consents, copyleft exposure | Data lineage records, licence terms, IP assignments | Customer data used for training without consent | Retrain, relicense or ring-fence affected models post-close |
| Cybersecurity | Posture, active incidents, shadow AI governance | Penetration tests, incident history, AI usage policy | Undisclosed incidents; no AI governance policy | Remediation priced as adjustment, indemnity or closing condition |
| Product and team | Roadmap dependencies, key-person concentration | Milestone dependency map, retention packages, contracts | Roadmap with no gating dependencies; unmapped key persons | Retention plan launches at signing, not after closing |
Evidence gaps and residual open questions
Evidence gaps are the honest residue of any compressed process. Carry them forward deliberately as a written register of residual open questions, each tagged with its treatment: a confirmatory diligence item before closing, a warranty in the purchase agreement, a specific indemnity, or a price adjustment. Deloitte's guidance points the same direction, calling for a living, auditable baseline across IP, data, infrastructure and talent rather than a point-in-time snapshot, because post-close evidence requests are inevitable. For PE and VC investment professionals running technology-heavy pipelines, the register is also the bridge between diligence and the integration plan, and the discipline of coordinating workstreams across a deal team is covered further in our AI in M&A deal teams workflow guidance.
This playbook is how Plausity structures technology-heavy transactions end to end: Technology Due Diligence for architecture, technical debt and scalability, AI Impact DD for capability and disruption exposure, Cybersecurity DD for posture and incident history, Commercial DD for pricing durability and retention quality, and AI for M&A for coordinating the workstreams into a single evidence register that survives from diligence to Day 1. Deal teams that want to see this playbook applied to a live transaction, from thesis to evidence register to integration view, can arrange a walkthrough with the Plausity team.
How Plausity accelerates this workflow
Plausity is an AI-native due diligence and deal intelligence workspace that helps M&A advisory firms, VC and PE funds, corporate development teams and investment-banking teams structure evidence, findings and questions across a data room. Plausity supports evidence extraction, source grounding, findings management and IC preparation — it does not replace human analysts, advisers or investment professionals, does not provide legal, tax, audit, regulatory or investment advice, and does not make autonomous investment decisions. All findings require human review. Built for today's investment and deal teams. Trusted by >200 firms.
To explore the underlying capabilities, see the Plausity AI analysis engine, findings and risk intelligence and evidence gap detection product pages, plus the IC memo and AI Q&A Assistant product pages. For team-level workflows, see how VC and PE funds and M&A advisory firms use Plausity across live deals, and how AI Impact due diligence, value creation, Tech DD and Commercial DD workstreams support the analysis.